
24/7 threat detection and active response
Already have tooling — and maybe a team? Passeca adds 24/7 detection engineering, threat hunting, and active response on top of the tools you already use.
Managed Detection and Response (MDR) by Passeca is 24/7 monitoring, detection engineering, threat hunting, and active response delivered on top of the security tools you already run.
For organisations in scope of NIS2, MDR can support incident-handling and cybersecurity risk-management processes with continuous detection, investigation, response and documented incident evidence.
We tune your detections, hunt for threats your tools miss, and contain confirmed threats under an agreed response playbook.
SOC-as-a-Service vs MDR: which do I need?
Both provide 24/7 detection and response. The difference is what you already have in place.
| SOC-as-a-Service | MDR | |
|---|---|---|
| What you already have | Limited security tooling or no SOC | Own tooling and/or a security team |
| Who provides the security platform | Passeca (PassIRP, CrowdStrike, Deception, and others) | Passeca works with your existing tools |
| What Passeca does | Runs the whole SOC for you | Adds detection engineering, threat hunting, and response to your existing tools |
| Best for | Building from scratch | Getting more from your existing security stack |


Not sure which fits? If you don't have a SIEM or security team, start with SOC-as-a-Service. If you already have security tools and a team, MDR adds 24/7 monitoring and response.
Detection engineering & threat hunting
Security tools generate alerts. The real value comes from tuning those detections and hunting for what they miss.
Detection engineering continuously improves your existing detections. Passeca writes, tunes and retires rules so your alerts focus on real threats. Our analysts maintain detection content against MITRE ATT&CK, map it to your assets, and suppress the noise that overwhelms in-house teams.
Threat hunting looks beyond those detections for threats your tools may miss — including malware-free intrusions, living-off-the-land techniques, and lateral movement that can precede ransomware encryption. Each hunt starts with a hypothesis, and its findings can lead to new detections in the platform.
What "response" actually means
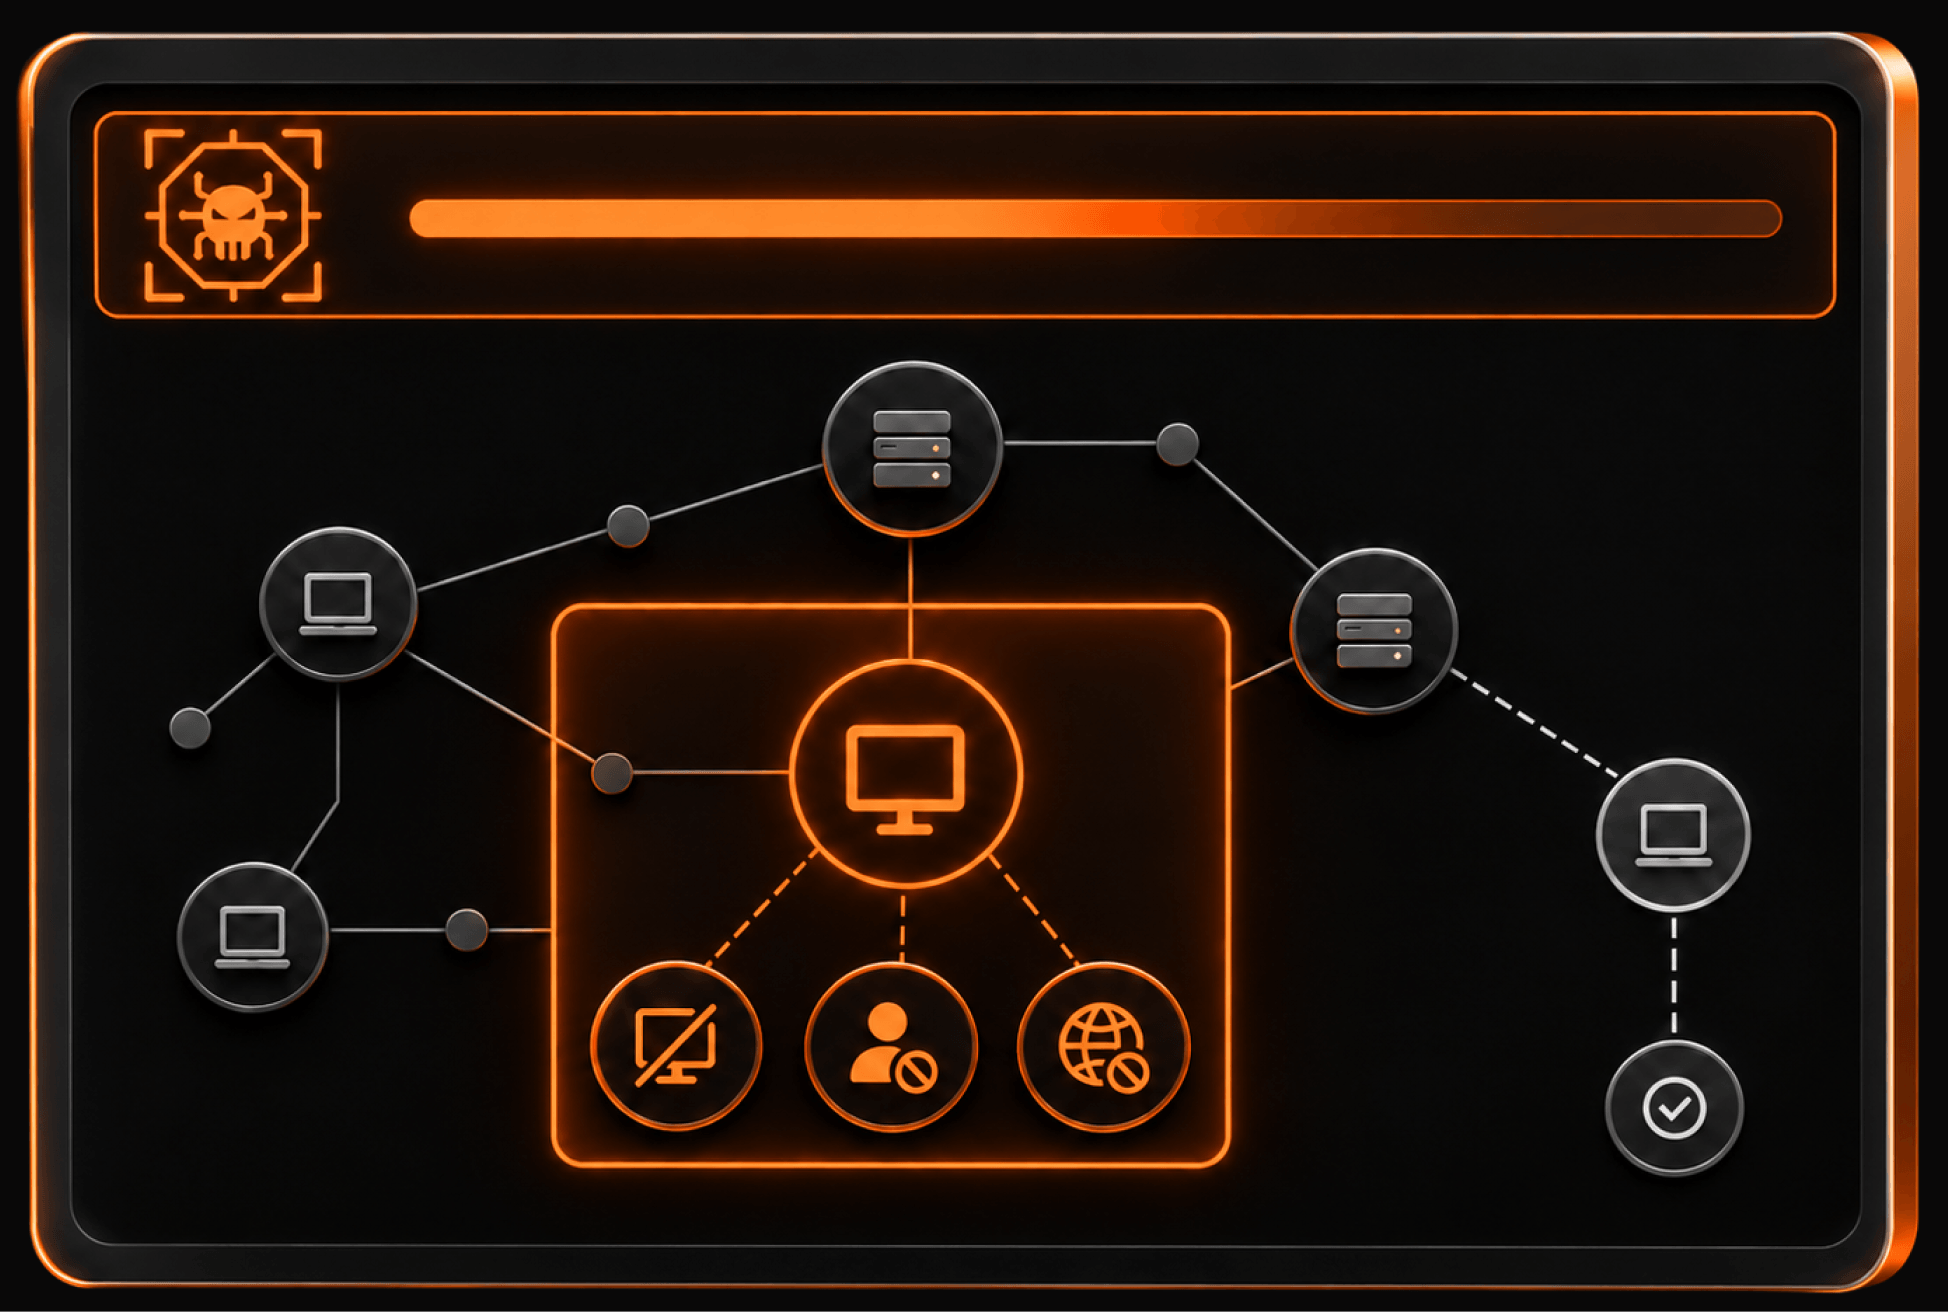
Before we respond autonomously, we agree exactly which actions Passeca can take and which require your approval.
When a confirmed threat requires immediate containment, Passeca can act within the limits you approve in advance:
- Isolate a compromised device to stop further network activity.
- Disable an account — stop a compromised user account from accessing systems.
- Block an indicator — block a malicious IP address, domain, or file hash.
Actions that could affect business availability, delete data, or have broader operational impact require your approval. We define and regularly review the boundary for autonomous response with each client, so you always know what Passeca can do and when we escalate to your team. These agreed response boundaries also give your organisation a documented incident-handling and escalation process that can support NIS2 readiness.
Bring your own tools
We work across the security stack you already have.
CrowdStrike
Endpoint security (EDR/XDR)

Wiz
Cloud security (CNAPP)

Rapid7
Attack surface management

Tenable
Exposure management

Enginsight
Vulnerability management

Your SIEM / SOAR
We work within your existing platform
Whatever your stack, PassAI-Guard adds an AI-powered triage layer. It classifies, deduplicates and scores alerts, then runs playbooks for routine containment. This lets analysts focus on genuine threats.
SLAs & reporting cadence
Performance against these targets is reviewed through regular operational reporting.
Detection & Containment
| Metric | Target |
|---|---|
| MTTD — High severity | 15–30 min |
| MTTR — Critical / High | ≤ 2 hrs |


Severity-based response
| Severity | Response target |
|---|---|
| Critical / P1 | ~15–30 min |
| High / P2 | ~30 min–4 hrs |
| Medium / P3 | ~4–24 hrs |
| Low / P4 | ~24–72 hrs |


MDR, answered
Clear answers to the questions that matter before you put your existing security stack under managed detection and response.
What is the difference between MDR and SOC-as-a-Service?
What can Passeca do without waking us up?
Which tools can you manage for us?
Passeca works with the security tools you already use, including:
- CrowdStrike — Endpoint security (EDR/XDR)
- Wiz — Cloud security (CNAPP)
- Rapid7 — Attack surface management
- Tenable — Exposure management
- Enginsight — Vulnerability management
- Your SIEM / SOAR — We work within your existing platform
- PassIRP — Passeca's SIEM and incident response platform
- PassAI-Guard — Passeca's AI-powered alert triage and security automation
The service is technology-agnostic, which means we can easily integrate your tools.
Do we still need our own security team?
What are the MDR SLAs?
How does PassAI-Guard fit into MDR?
How much does MDR cost?
Once we start MDR, how does Passeca keep us informed?
What should we look for in an MDR provider?
How is MDR different from antivirus or EDR?
What does MDR take off our internal team's workload?
What should we look for in an MDR provider in Germany?
Look for an MDR provider that understands your regulatory and operational environment, can work with your existing security stack, and offers clear responsibilities for detection and response. For German organisations, also consider data residency, security certifications, contractual requirements, and the provider's ability to support regulated environments.
For instance, Passeca also provides compliance services to help organisations address European regulatory requirements such as DORA and NIS2 and connect them with their wider security and governance programme.
What challenges should I expect when implementing an MDR solution?
How does Passeca MDR support NIS2 readiness?
Can Passeca MDR help with Cyber Resilience Act requirements?
Already invested in tooling? Make it work 24/7.
We'll review your stack, show you where detection and response gaps remain, and outline an MDR approach that fits your environment.
Related