
Your SOC. No in-house team required.
We provide an AI-powered security operations platform backed by threat intelligence and experienced analysts for continuous monitoring, threat detection, and incident response across your environment.
Passeca SOC-as-a-Service gives you the people, technology and expertise to run 24/7 security operations without the cost and complexity of an in-house SOC.
We protect your endpoints, cloud, network and identity with threat detection, investigation and incident response.
Our SOC specialists combine:
- Security information and event management (SIEM)
- AI-assisted triage and automation
- Endpoint detection and response (EDR)
- Deception technology
- Threat intelligence
- Experienced security analysts
- 1
Monitoring
Your endpoints, cloud, network and users stay under 24/7 security monitoring.
- 2
Threat detection
AI, security analytics and threat intelligence help identify potential threats.
- 3
Data analysis
Our analysts investigate alerts and validate whether a threat is genuine.
- 4
Incident response
Confirmed threats are investigated, contained and handled by our security team.
- 5
Reporting
Every incident is documented, with findings used to improve detection and response.
In-house SOC vs SOC-as-a-Service
Building a SOC means hiring analysts around the clock, buying and tuning a SIEM, and retaining people in a fiercely competitive market. SOC-as-a-Service trades that build for a subscription.
A 24/7 Security Operations Center needs skilled analysts, security technology and round-the-clock coverage. Meanwhile, 45% struggle to hire cybersecurity talent, according to ENISA.
The cost adds up too. An in-house SOC can cost up to 71% more than a managed SOC over three years — $2.0M–$6.1M vs. $550K–$1.8M.
| In-house SOC | SOC-as-a-Service by Passeca | |
|---|---|---|
| Upfront cost | Technology, infrastructure, setup | Onboarding only — platform included |
| Time to value | 6–18 months | ~4 weeks |
| 24/7 coverage | Hire and retain shifts | Included |
| Staffing risk | Attrition, holidays, sick leave | Passeca carries the risk |
| Detection engineering | Build and maintain rules | Passeca handles detection and tuning |
| Threat intelligence | Buy and integrate separately | Signals, Passeca’s threat intelligence platform, is included |
| Tooling | Procure, integrate, renew | PassIRP, PassAI-Guard, CrowdStrike, Deception* |
| Cost over 3 years | $2.0M–$6.1M* | Lower and predictable* |


*Costs vary by organisation size, scope and technology stack. Tooling is subject to the agreed service scope.
What your SOC by Passeca includes
One subscription for end-to-end security: Passeca’s security monitoring and AI automation platforms, endpoint protection, deception, threat intelligence, and 24/7 analysts who run it all.
PassIRP (SIEM)
Log ingestion, correlation, detection and incident case management with EU data residency.
PassAI-Guard (AI triage + SOAR)
AI-assisted alert triage, automated enrichment and SOAR playbooks that contain, isolate and ticket threats.
CrowdStrike EDR
Endpoint detection and response on the CrowdStrike Falcon platform, monitored 24/7.
Passeca Deception
Decoy systems and credentials that expose attackers before they reach critical assets.
Signals threat intelligence
Dark web, leaked-credential and infostealer-log monitoring, plus ransomware leak-site tracking.
24/7 analysts
Certified security analysts on continuous shift — detection engineering, threat hunting and incident response.
What we monitor 24/7
Passeca monitors your entire environment, from employee devices and cloud systems to networks, identities and operational technology.
 Endpoints — workstations, servers and mobile devices.
 Cloud — AWS, Azure and GCP environments.
 Network — firewalls, VPN, DNS and network traffic.
 Identity — user accounts, access and suspicious login activity.
 OT / SCADA — operational technology and industrial environments.
Our SLAs
Security operations need clear targets. Our SLAs define how quickly Passeca detects, responds to and escalates security incidents — with 24/7/365 service availability.
| Metric | Target | Measurement |
|---|---|---|
| Mean time to detect (MTTD) — High severity | 15–30 min | Time from event to validated detection |
| Mean time to respond (MTTR) — Critical / High | ≤ 2 hrs | Time from detection to active containment |
| Critical-severity response (P1) | ~15–30 min | Confirmed incidents, immediate escalation |
| High-severity response (P2) | ~30 min–4 hrs | Targeted response within the committed window |
| Medium-severity response (P3) | ~4–24 hrs | Severity-based response |
| Low-severity response (P4) | ~24–72 hrs | Severity-based response |
| Availability | 24/7/365 | Security operations available around the clock |


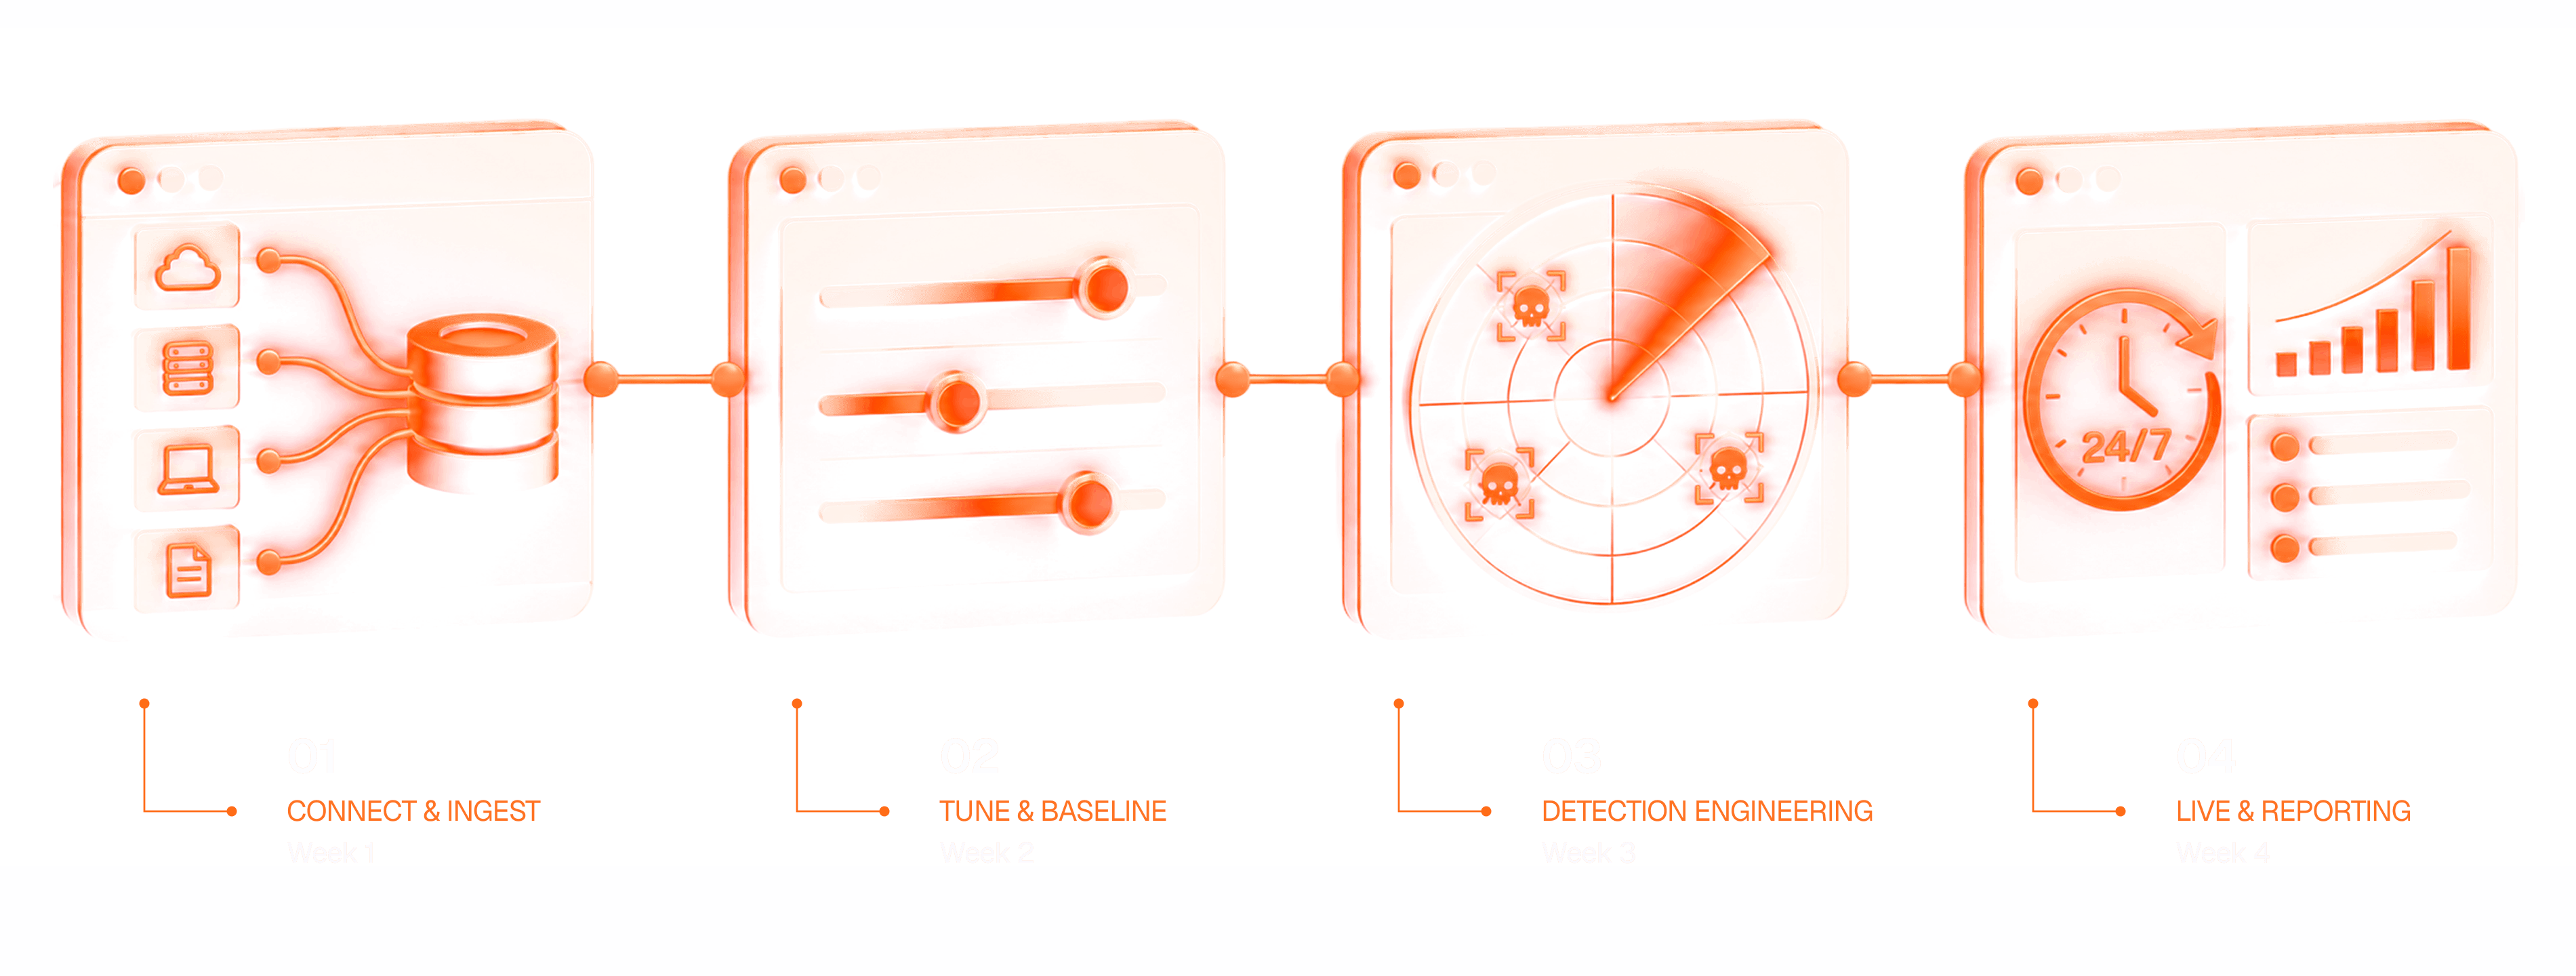
From signed to live in four weeks
- 01
Week 1 — Connect your environment
We connect your key systems to PassIRP, protect your endpoints with CrowdStrike Falcon and set up secure analyst access. By the end of week one, we have visibility across your environment.
- 02
Week 2 — Tune & reduce noise
We tune your security monitoring to reduce false alarms and focus on real threats. PassAI-Guard begins to assess and prioritise alerts.
- 03
Week 3 — Tailor your detection
We tailor threat detection to your environment and risk profile, deploy Passeca Deception and test the escalation process with your team.
- 04
Week 4 — Go live
The service is fully live 24/7. You receive your first operational report, agree the reporting schedule with your account team, and confirm the SLAs and escalation paths in writing.
How does the Passeca SOC support compliance?
A Passeca SOC can support relevant requirements across ISO 27001, SOC 2, DORA, NIS2 and the CRA. Continuous monitoring, detection, incident records and response reports provide evidence that can support your wider compliance programme.
ISO 27001
PassIRP offers logging, monitoring and incident records to support A.8.15, A.8.16 and A.5.24.
SOC 2
Passeca provides 24/7 monitoring, alert handling and incident records to support CC7 requirements for system monitoring and anomaly detection.
DORA
Passeca enables incident detection, classification and records to support Articles 17–23 on ICT-related incident management and reporting.
NIS2
Passeca supports incident handling under Article 21 and provides investigation records, timestamps and response evidence that can support the Article 23 incident-reporting process, including the 24-hour early warning and 72-hour incident notification.
Cyber Resilience Act (CRA)
For manufacturers in scope, Passeca can help detect and investigate security incidents and preserve evidence that supports CRA reporting. Product-security and vulnerability-handling requirements still require controls beyond the SOC.
SOC-as-a-Service, answered
What is the difference between SOC-as-a-Service and an in-house SOC?
What does SOC-as-a-Service cost?
Pricing depends on the size of your environment and the level of coverage you need. We scope the service based on your endpoints, cloud accounts and log sources. For more information, you can book a consultation with our team.
How quickly will you detect and respond to an incident?
Where is my data stored?
Do I still need my own security team?
Which compliance frameworks does SOC-as-a-Service help with?
Can you monitor our existing CrowdStrike or EDR deployment?
Yes. CrowdStrike Falcon is part of the standard service, and if you already own EDR or other tools, our MDR service can monitor and respond on top of them. See our MDR page for the technology-agnostic, bring-your-own-tools model.
How long does onboarding take?
A standard onboarding takes around four weeks. We connect your systems, set up monitoring, tune the service to your environment and prepare your security team for 24/7 monitoring and response. Larger or more complex environments may take longer to set up.
How does SOC-as-a-Service improve cybersecurity for small businesses?
What are the key features of SOC-as-a-Service solutions?
How does an outsourced SOC protect my company?
Can SOC-as-a-Service integrate with existing SIEM tools?
Can SOC-as-a-Service make us NIS2 or CRA compliant?
Don't build a SOC — subscribe to one.
Book a free consultation. Tell us about your environment, security needs and compliance requirements, and we’ll scope a SOC-as-a-Service that can go live in weeks.
Related