
Strategic security leadership, from €1,950/month
Get a named vCISO to lead your security strategy, risk and compliance — without the cost of hiring a full-time CISO. Plans start from 10 hours a month.
A Virtual CISO is a senior security leader who provides strategic cybersecurity leadership on a flexible, part-time basis.
From €1,950/month, you get a named vCISO who leads your security strategy, risk management, compliance programme and executive reporting — backed by Passeca's wider security and compliance team.
Three tiers, from €1,950/month*
Every plan includes a named vCISO. Choose your tier based on how much hands-on support you need each month.
Basic
Startups and SMEs establishing a security programme for the first time.
- Your named vCISO
- Security strategy & roadmap
- Risk register & treatment plan
- Quarterly executive reporting
- Core security policies and standards
- Email and call support between sessions
Advanced
Most popularFor growing organisations managing compliance and a more complex security programme.
Everything in Basic, plus:
- Ongoing leadership of your compliance programme (ISO 27001, SOC 2, NIS2)
- Supplier and third-party risk oversight
- Incident-response planning and tabletop exercises
- Regular working sessions with your management team
Enterprise
Larger or regulated organisations needing near-full-time strategic security leadership.
Everything in Advanced, plus:
- Board-level security leadership
- Multi-framework programme (ISO 27001 + SOC 2 + sector)
- Direct access to Passeca security specialists
- Incident-response leadership during events
- Security oversight for M&A and major projects
*All tiers are month-to-month retainers, scalable at the quarterly business review.
vCISO vs full-time CISO vs consultant
The decision buyers make when they need security leadership but cannot justify a full-time executive.
| vCISO | Full-time CISO | Consultant | |
|---|---|---|---|
| Ongoing security leadership | Yes | Yes | Often project-focused |
| Named, accountable lead | Yes | Yes | Depends on engagement |
| Typical monthly cost | €1,950+ /mo | €12,500+ /mo salary | Day rate / project fee |
| Cost model | Flexible monthly retainer | Full salary + benefits | Per day or engagement |
| Flexible hours (scale up/down) | Easily | Limited | Depends on scope |
| Access to specialist expertise | Built in | Requires internal hires | Depends on consultant/team |
| Board-ready reporting | Included | Included | Sometimes |
| Owns programme long-term | Ongoing | Ongoing | Usually project-based |
| Time to get started | Days to weeks | 3-6 month hire | Often days to weeks |
| Best for | SMEs and mid-market teams | Larger enterprises | One-off projects |


Think of a vCISO as the middle ground between a permanent executive hire and a project-based consultant: senior, ongoing leadership that can scale with the business.
What your Passeca vCISO takes care of
Your exact scope depends on your plan and priorities. These are the areas your vCISO can lead for you.

Security strategy & roadmap
A multi-year strategy tied to your business goals, with clear priorities and milestones.

Risk management
Continuous identification, evaluation and treatment of risk across people, process and technology.

Compliance oversight
Leadership of your ISO 27001, SOC 2, NIS2 or DORA programme, bringing in Passeca specialists where needed.

Governance & policy
Clear security policies, standards and decision-making processes that people can actually follow.

Incident-response planning
Clear incident-response plans, defined roles and tabletop exercises so everyone knows what to do when something goes wrong.

Third-party risk
A risk-based approach to onboarding, monitoring and offboarding critical ICT suppliers.

Security awareness
Role-aware training and phishing simulation through PassHRM, with a measurable human-risk score.

Executive reporting
Crisp, board-ready reporting in business language that gives leadership the context to decide.

Vendor & tooling decisions
Independent guidance on which security technologies to buy, and how to implement them.
How Passeca's vCISO service works
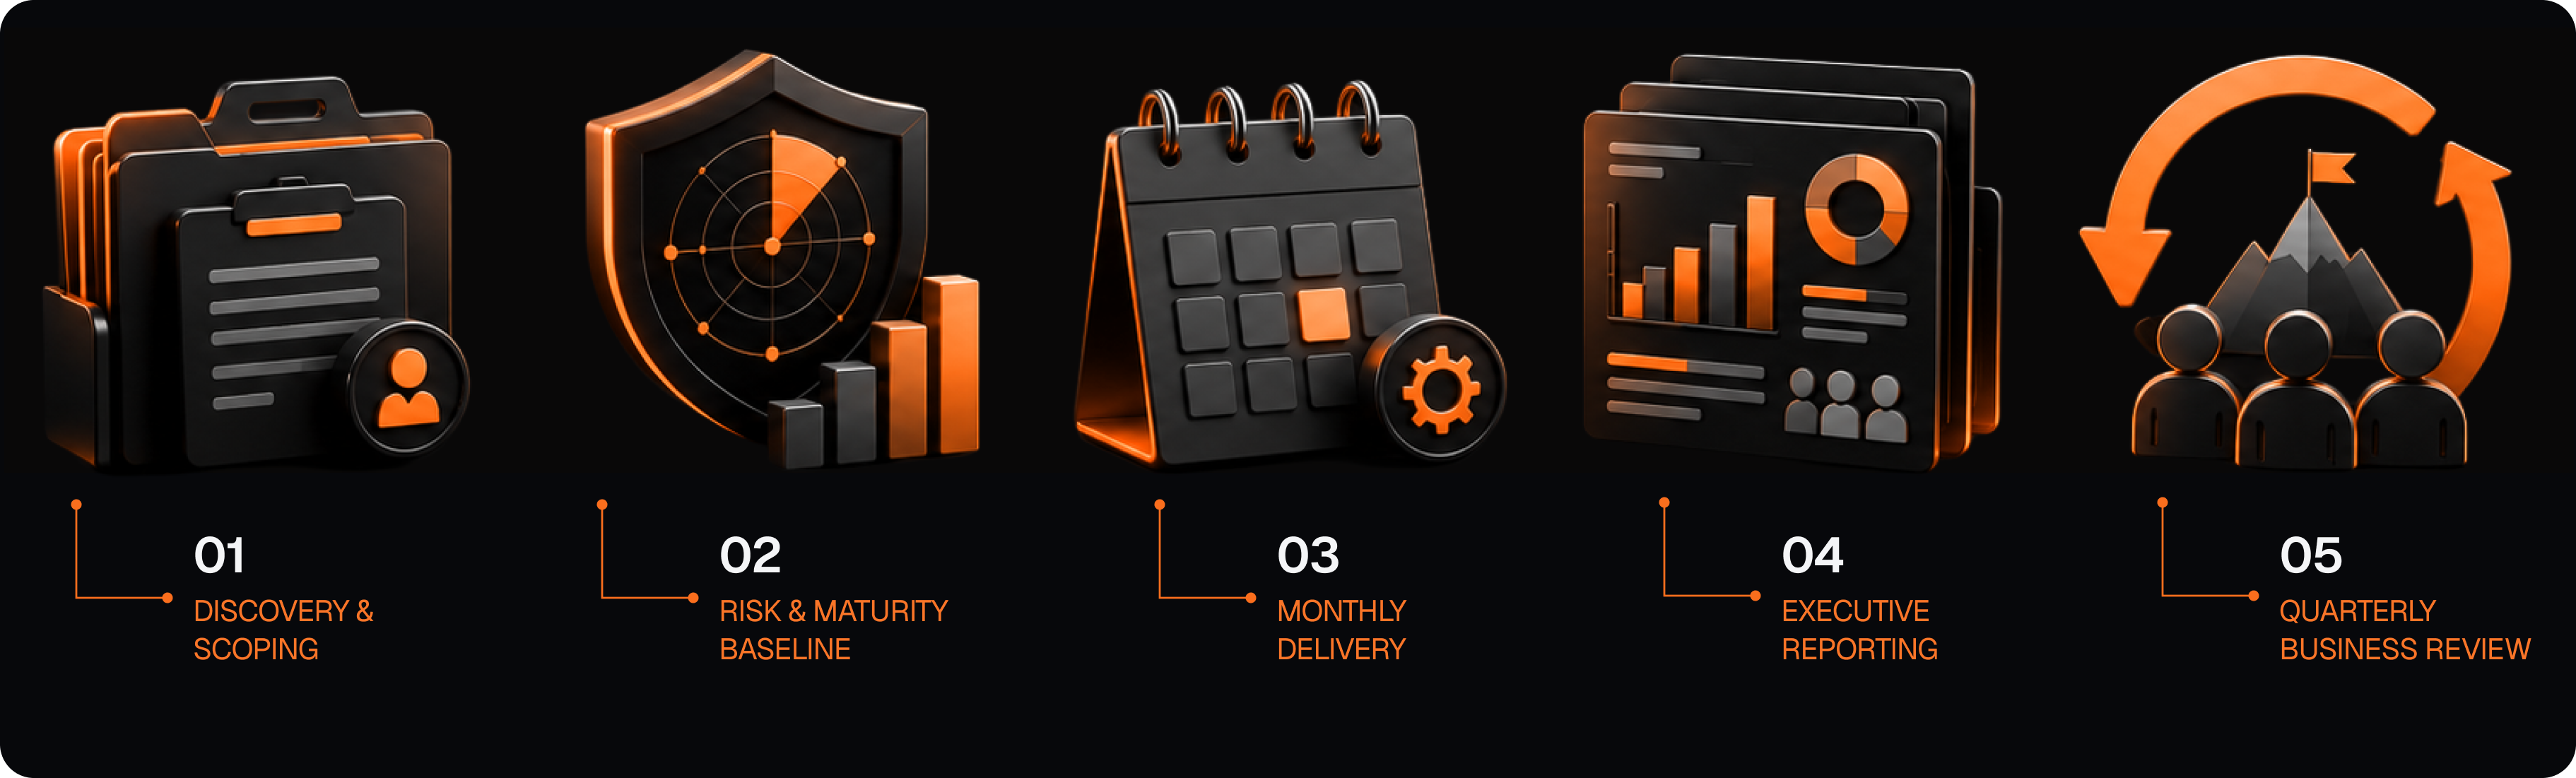
A clear cadence from discovery to quarterly review — you always know what the vCISO is doing and why.
- 01
Discovery & scoping
We learn how your business works, what you need to protect and which regulatory requirements matter (ISO 27001, SOC 2, NIS2, DORA and the Cyber Resilience Act (CRA)). Together, we define your vCISO's role and scope.
- 02
Risk & maturity baseline
We assess your current risks and security maturity, then turn the findings into a prioritised roadmap — the working document the vCISO executes against each month.
- 03
Monthly delivery
Your vCISO turns the roadmap into action every month, focusing their time on the priorities that matter most.
- 04
Executive reporting
You receive board-ready reporting on a defined cadence, covering risk posture, roadmap progress, regulatory status and incidents.
- 05
Quarterly business review
Every quarter, we review progress, reset priorities and make sure your level of support still fits. Scale up or down when needed.
One named vCISO. Backed by a full security team.
The person leading your security matters as much as the plan you choose. That's why every engagement is led by a named vCISO with relevant security and sector experience — someone who gets to know your business, leads your priorities and keeps your security programme moving forward.
Behind them is Passeca's wider team of compliance specialists, auditors and security analysts, ready to provide deeper expertise whenever it's needed. You still have one senior lead, with the strength of a wider team behind them.
How we match you
- 01
Scoping
We learn your business, risks and frameworks.
- 02
Matching
We propose a vCISO matched to your sector and frameworks.
- 03
Meet before you commit
You meet them in the consultation before signing.
Certifications we require
Your vCISO profile
Every Passeca vCISO meets the same bar:
- 10+ years in security, with at least 5 in a leadership or advisory role
- Holds at least one of CISSP, CISM or CISA, plus ISO 27001 Lead Auditor or Lead Implementer where your programme needs it
- Hands-on experience with ISO 27001, NIS2 and DORA programmes
- Matched to your sector and language (DE / EN)
You meet your vCISO before you sign. We introduce them in the consultation, so you can judge the fit yourself.
Mid-sized SaaS company, ~120 staff: ISO 27001 certified in 9 months with a Basic-tier vCISO.
Virtual CISO, answered
The questions buyers ask before choosing a vCISO partner.
What is a Virtual CISO (vCISO)?
How much does a vCISO cost?
How does a vCISO compare to a full-time CISO?
What hours do I get per month?
Do we work directly with our vCISO?
Can a vCISO lead our ISO 27001 or SOC 2 programme?
Can we start small and scale up?
How quickly can a vCISO start?
What does a vCISO actually do?
How can a vCISO fill a security leadership gap?
Is a vCISO suitable for startups and small businesses?
How do I choose the right vCISO?
What is the difference between a vCISO and an MSSP?
Can Passeca's vCISO lead our NIS2 programme?
Can Passeca's vCISO support Cyber Resilience Act readiness?
Get your senior security leader from €1,950/month
Start with a free consultation. We'll learn about your current setup, priorities and compliance needs, and introduce you to the person who could lead your programme.