Managed Security Service Provider

One cybersecurity partner for compliance, testing, and 24/7 defence.

We deliver governance and compliance, penetration testing, managed security, incident response, and threat intelligence through our own security technology and AI-powered automation, alongside carefully selected partner solutions.
Glowing orange mechanical bee standing on a keyboard key labelled Passeca
ISO 27001
Certified across Germany, Switzerland and the UK
4
Proprietary platforms
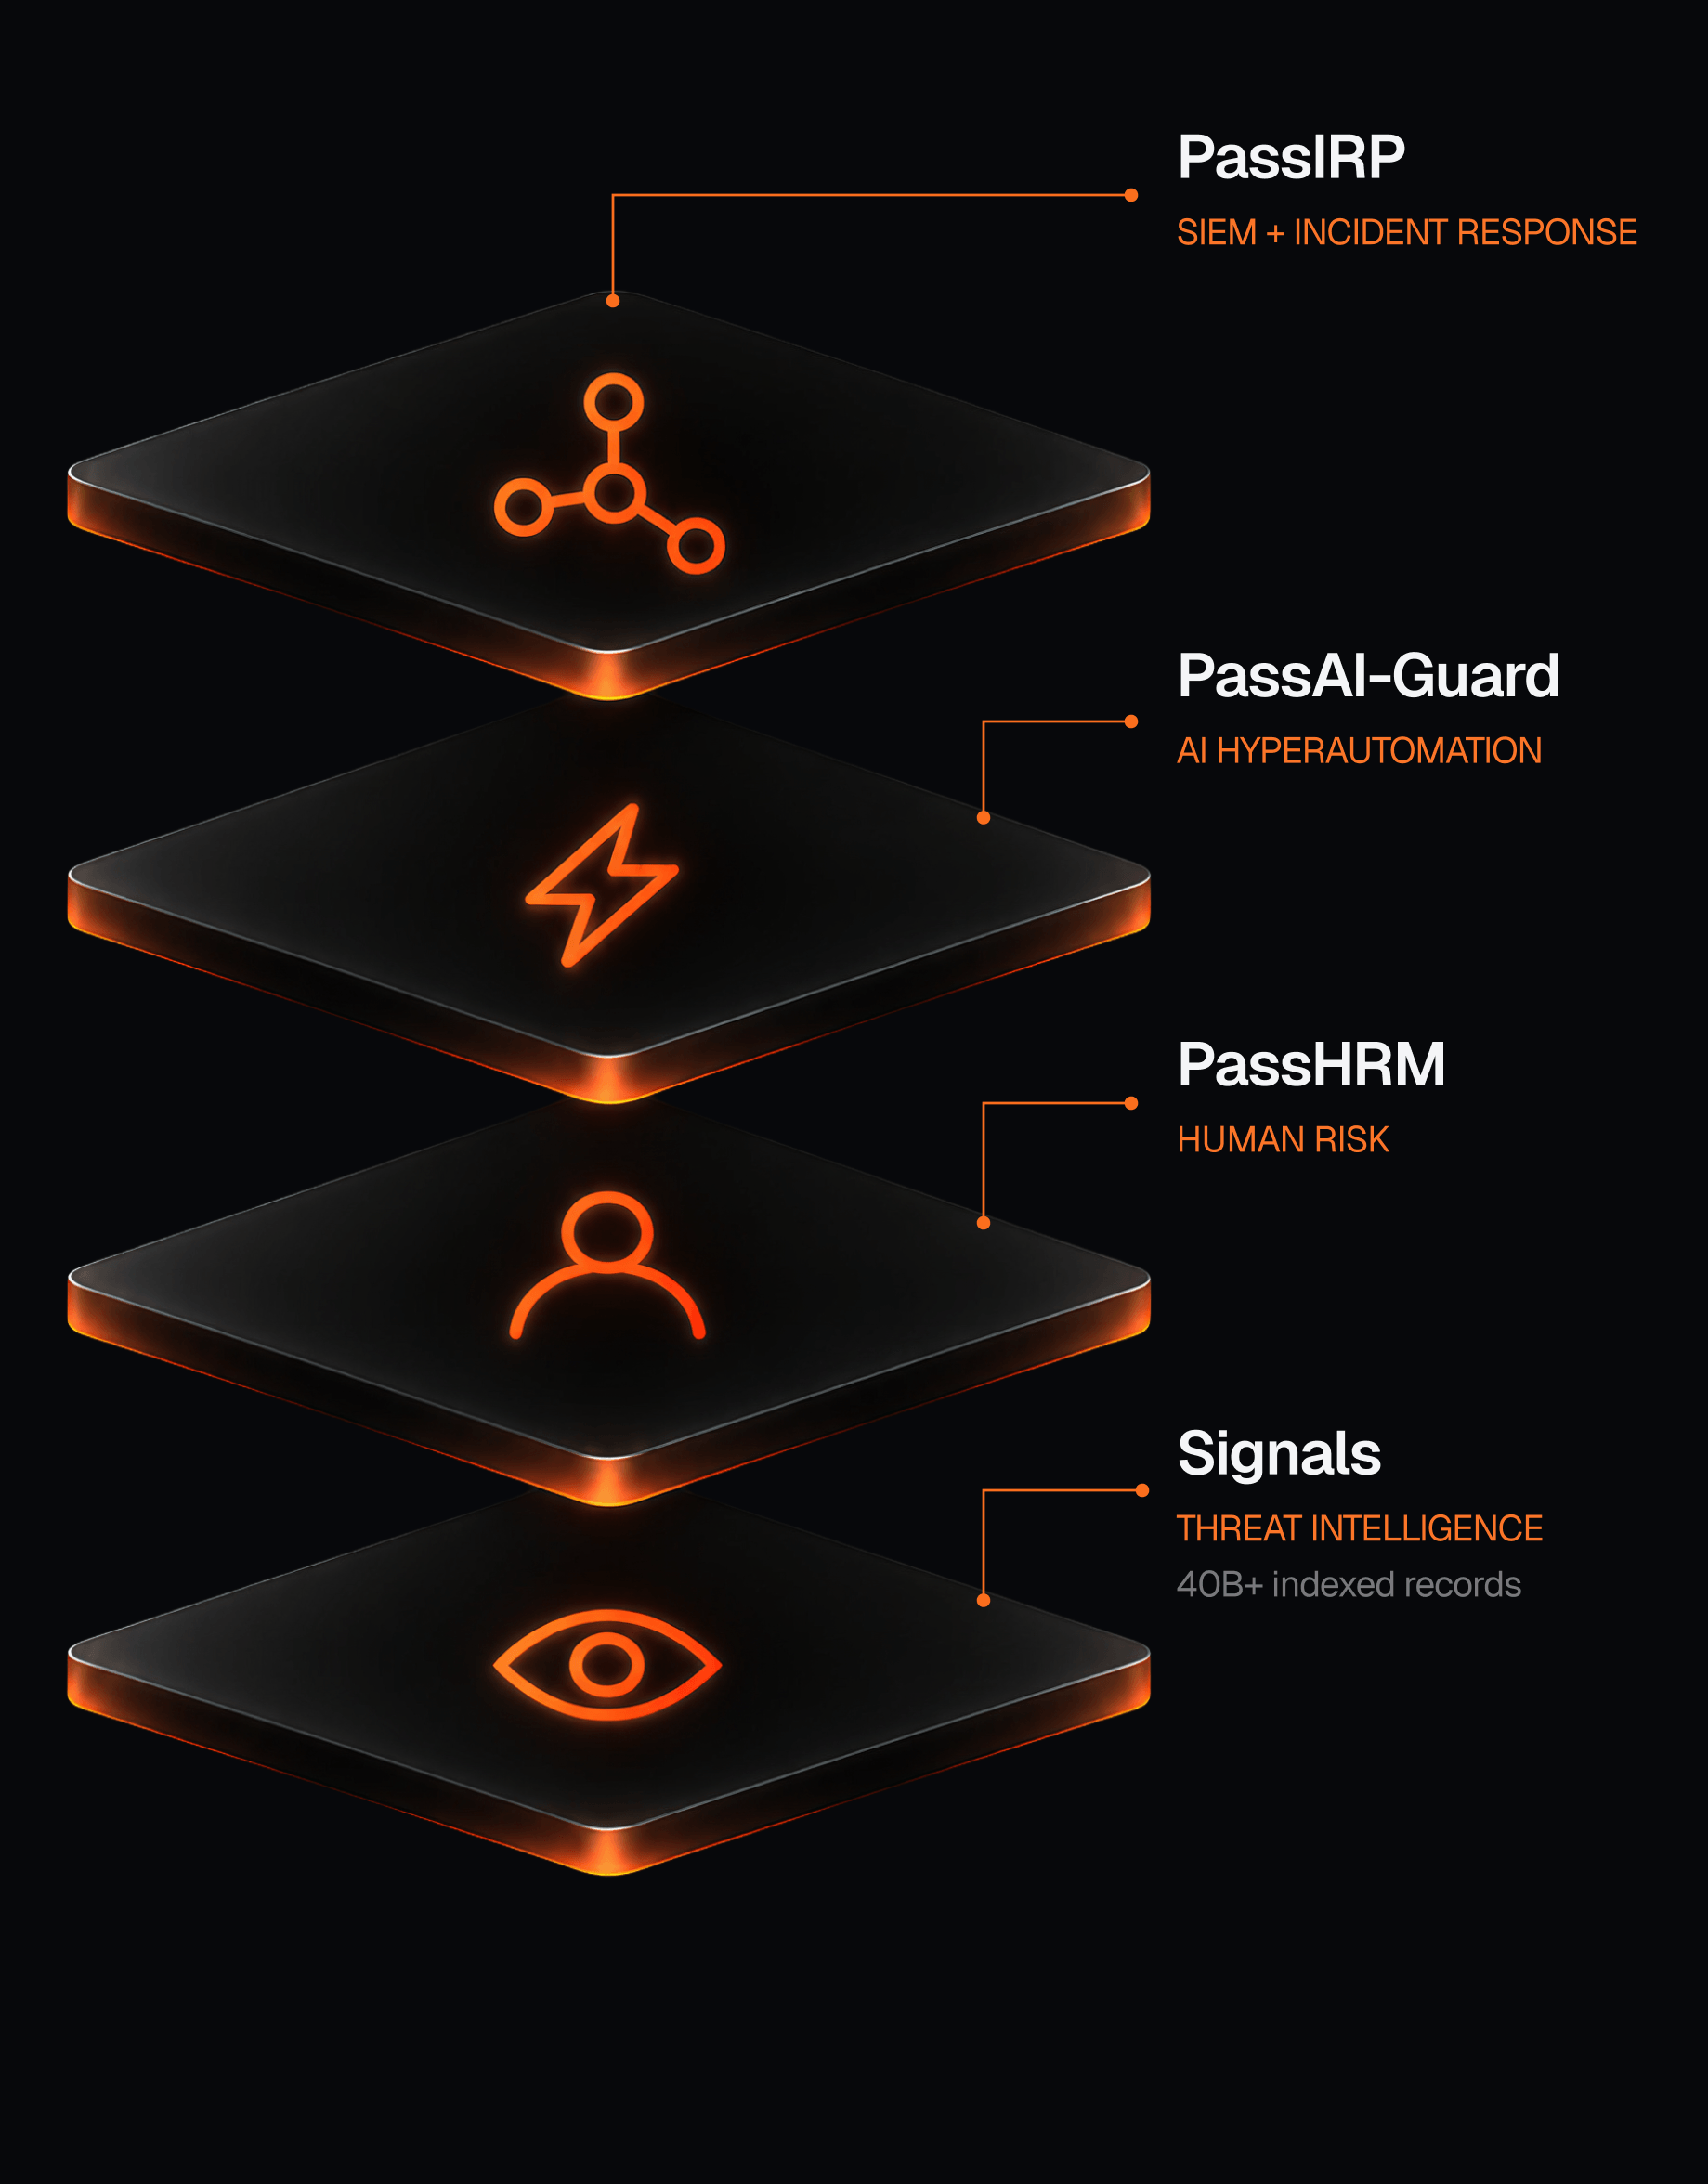
PassIRP, PassAI-Guard, PassHRM, Signals
11
Technology partners
Hyperproof, Halcyon, CrowdStrike, Wiz, and others
24/7
Security monitoring and incident response

Passeca is a German cybersecurity provider delivering governance and compliance (ISO 27001, SOC 2, TISAX, NIS2, DORA), penetration testing, SOC-as-a-Service and MDR, incident response and threat intelligence โ€” on its own SIEM (PassIRP) and AI automation platform (PassAI-Guard), with a best-of-breed partner stack.

Start with your goal

What do you need today?

Choose your current security priority and find the next right step.
Get certified

I need to get certified

ISO 27001, SOC 2, TISAX, NIS2, DORA, and seven more frameworks โ€” gap analysis to certification, accelerated on Hyperproof.

Explore
Test my defences

I need to know if we're hackable

Penetration testing across web, API, mobile, cloud, network and Wi-Fi. OWASP and PTES methodology, a real report, free retest.

Explore
Monitor 24/7

I need someone watching around the clock

SOC-as-a-Service and MDR on our own SIEM (PassIRP) and AI automation layer (PassAI-Guard). Published MTTD and MTTR SLAs.

Explore

Certified expertise across the security stack
  • Certified Information Systems Security Professional โ€” ISC2
  • Offensive Security Certified Professional โ€” OffSec
  • Offensive Security Experienced Penetration Tester โ€” OffSec
  • Offensive Security Web Expert โ€” OffSec
  • Certified Ethical Hacker โ€” EC-Council
  • Certified Hacking and MITRE SOC Analyst โ€” EC-Council
  • Certified Penetration Testing Professional โ€” EC-Council
  • Licensed Penetration Tester Master โ€” EC-Council
  • eLearnSecurity Mobile Application Penetration Tester โ€” INE
  • eLearnSecurity Web Application Penetration Tester eXtreme โ€” INE
  • Certified Information Systems Auditor โ€” ISACA
  • Certified Information Security Manager โ€” ISACA
  • Certified in Risk and Information Systems Control โ€” ISACA
  • ISO/IEC 27001 Lead Auditor โ€” PECB / BSI
  • ISO/IEC 27001 Lead Implementer โ€” PECB / BSI
  • ISO/IEC 27005 Certified Risk Manager โ€” PECB
  • AWS Certified Security โ€“ Specialty โ€” Amazon Web Services
  • CREST Registered Tester โ€” CREST
  • CREST Practitioner Security Analyst โ€” CREST
  • Google Cloud โ€” Advanced Red Team Certification โ€” Google
  • Google Cloud Professional Cloud Security Engineer (Red Team) โ€” Google
  • Microsoft Cybersecurity Architect (Red Team) โ€” Microsoft
  • Cloud Attack and Red Team Certification โ€” OffSec
  • AI Red Team Professional โ€” SecOps
  • Certificate of Cloud Security Knowledge โ€” Cloud Security Alliance
  • BSI C5 โ€” Cloud Computing Compliance Controls Catalog โ€” BSI (Germany)
  • SOC 2 / AICPA Trust Services Criteria โ€” AICPA
  • TISAX โ€” Trusted Information Security Assessment Exchange โ€” ENX / VDA
  • GDPR compliance โ€” European Union
  • NIS2 Directive compliance โ€” European Union
  • Payment Card Industry Data Security Standard โ€” PCI SSC
  • PCI DSS Security Standards Assessor โ€” PCI SSC
  • ISO/IEC 27017 & 27018 โ€” cloud security & PII โ€” ISO/IEC
  • ISO/IEC 42001 โ€” AI Management System โ€” ISO/IEC
Technology-agnostic

A carefully selected partner ecosystem

Our technology ecosystem includes leading platforms across endpoint, cloud, vulnerability, GRC, and threat intelligence.

See the full stack
Why Passeca

One partner for end-to-end security

We bring the security lifecycle together โ€” from governance and testing to detection and response.

One partner, full lifecycle

Governance, offensive security, threat intelligence, managed security operations, and incident response under one roof.

Technology-agnostic by design

Hyperproof, Halcyon, CrowdStrike, Wiz, Tenable, Rapid7, Aikido, Enginsight, bare.ID, ThreatModeler and Panorays โ€” the right tool for each job.

Human expertise, amplified by AI

PassAI-Guard handles routine alert triage and enrichment, while our certified analysts (CISSP, OSCP, ISO 27001 Lead Auditor) focus on threats that require human judgment.

European roots, global delivery

Founded by professionals from Germany, Switzerland and Ukraine. ISO/IEC 27001:2022 certified across all three locations, with EU data residency.

What clients say

Trusted across FinTech, e-commerce, and platforms

Passeca guided us through ISO 27001 from zero to certified in under a year. Pragmatic, business-aligned, and genuinely invested in our outcome.
Alex F.CIO ยท FinTech company
The gap analysis alone was worth the engagement. We finally had a clear picture of what was missing and a prioritised plan to close it.
Andreas J.Head of Information Security ยท E-commerce company
Their team felt like an extension of ours โ€” responsive, knowledgeable, and a genuine partner in our security programme.
Denis E.Co-Founder ยท Talent matching platform
FAQ

Frequently Asked Questions about Passeca

What is Passeca?
Passeca is a European cybersecurity company that helps organisations manage security from strategy and compliance through to testing, monitoring, threat detection and incident response. We combine our own security technology, AI-powered automation and specialist teams with carefully selected partner solutions to support both day-to-day security operations and longer-term security programmes.
What cybersecurity services does Passeca provide?
Passeca provides cybersecurity governance and compliance, penetration testing, managed security operations, Managed Detection and Response (MDR), threat intelligence and Incident Response. We also build our own security technology to support monitoring, automation, threat detection and security awareness.
Can Passeca work with the security tools we already use?
Yes. Passeca is technology-agnostic and can work with your existing security stack where it makes sense. Our managed security services can integrate with the tools you already use, while our team can also recommend or provide additional technology where there are gaps.
Which cybersecurity standards and regulations can Passeca support?
Passeca supports organisations working towards requirements such as ISO 27001, SOC 2, NIS2 and DORA, as well as Cyber Resilience Act readiness where the regulation applies to their products. We help connect regulatory and assurance requirements to the policies, technical controls, monitoring, testing and response processes that support them.
How can Passeca help with NIS2?
Passeca can support NIS2 readiness across areas including cybersecurity risk management, governance, incident handling, security monitoring, vulnerability management, supplier risk and incident-response planning. Depending on your needs, this can combine compliance support with services such as penetration testing, SOC-as-a-Service, MDR and Incident Response.
How can Passeca help with the Cyber Resilience Act?
For organisations that manufacture or provide products with digital elements, Passeca can support CRA readiness across areas such as cybersecurity risk assessment, vulnerability management, security testing, incident-response preparedness and security governance. We can also help connect product-security requirements with the wider security processes and technical controls behind them.
How does Passeca support DORA?
Passeca helps financial organisations address operational security requirements under DORA through services including ICT risk and compliance support, security testing, continuous monitoring, threat detection, incident response and resilience planning. We can help connect governance requirements with the operational security capabilities used to support them.
Can Passeca help with ISO 27001 or SOC 2?
Yes. Passeca can support ISO 27001 and SOC 2 programmes from initial readiness and gap assessment through policy and control implementation, security testing, evidence preparation and ongoing security operations. The exact scope depends on your current maturity and the requirements you need to address.
Does Passeca provide 24/7 cybersecurity support?
Yes. Passeca provides 24/7 security monitoring and threat detection, plus incident response. Depending on the service, our team can investigate alerts, hunt for threats, contain confirmed incidents and escalate issues according to an agreed response process.
Can Passeca help if we do not have an internal security team?
Yes. Services such as SOC-as-a-Service and vCISO are designed for organisations that need additional security capability without building a full internal team. Passeca can provide operational security coverage, senior security leadership or specialist support depending on what you need.
Can Passeca support our internal security team?
Yes. Passeca can work alongside existing IT and security teams rather than replacing them. For example, MDR can add 24/7 detection and response to your existing tools, while a vCISO can provide senior security leadership and our specialists can support areas such as compliance, penetration testing, threat intelligence or incident response.
What happens if we have an active security incident?
Passeca's Incident Response team helps contain, investigate and recover from serious security incidents such as ransomware, account compromise, data breaches and intrusions. For organisations that want response arrangements in place before an incident occurs, we also offer Incident Response retainers.
Does Passeca offer penetration testing?
Yes. Passeca provides penetration testing and offensive security services to identify weaknesses before attackers can exploit them. Testing can form part of a wider security programme, support compliance requirements or focus on specific systems and applications.
Always-on defence

Could your business survive a major cyber attack?

Don't wait to find out. Book a free consultation โ€” tell us your goals and we'll respond within one business day with a tailored action plan.